The Broadcom Wi-Fi flaw that sat in router code for 16 years isn’t only a Belgian problem. The researcher who disclosed it has now flagged gateways from AT&T, CenturyLink, Frontier and Comcast’s Xfinity, based on scans of their firmware.
None of those US models has been shown to be hacked, and no attacks in the wild have been confirmed. The catch is that the fix depends on your internet provider or router maker. Broadcom has also declined to issue the tracking number that usually pushes companies to patch.
A Belgian demo, then a list that kept growing
Quentin Kaiser, a Belgian security researcher, presented the bug at the Hexacon conference in Paris on October 16. He published a long write-up on his blog the same day. The bug sits in Broadcom’s code for Wi-Fi Protected Setup, or WPS. That’s the feature that lets a device join a network with a button press instead of a password.
Kaiser writes that the code has been in Broadcom’s software kit “since at least 2010.” Someone within Wi-Fi range doesn’t need your network password to reach it, he says. He showed it working on gateways from three Belgian providers: Proximus, VOO and Orange.
In one demo he pulled the saved Wi-Fi password off an Orange Belgium box. In another he took control of a Proximus gateway.
His rough estimate for Belgium is about 1.56 million affected gateways, a figure he holds with “medium confidence.” Early coverage, including Cyber Security News, centred on those Belgian devices. But Kaiser’s detection toolkit on GitHub now lists about 260 entries from 29 manufacturers. It warns that the list “is not exhaustive.”
The US gateways on Kaiser’s list
We went through that list line by line on October 23. Nineteen entries name a US internet provider. Kaiser added most of them on October 22 and 23, after running his detection rules against firmware files. Several of those files came from the providers’ own support pages.
| Provider | Gateway models listed | What the firmware scan found |
|---|---|---|
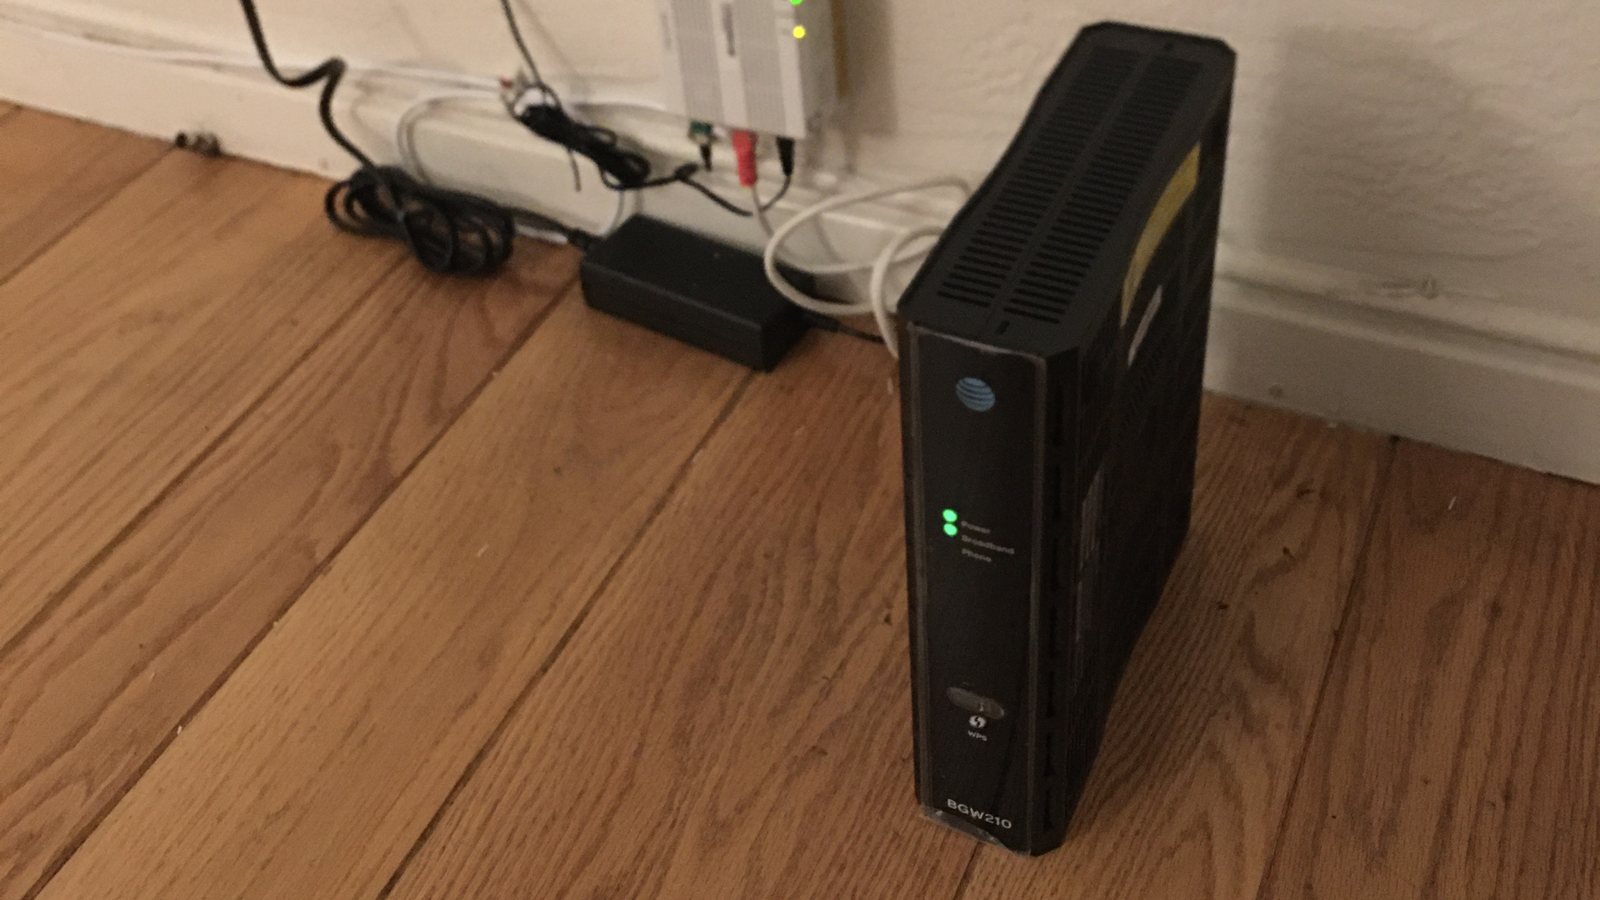
| AT&T | ARRIS BGW210-700, NVG589, NVG599 | Code matching the vulnerable pattern |
| AT&T | Nokia BGW320-505 | Broadcom’s WPS component, but no match for the flaw (one older firmware checked) |
| CenturyLink | Actiontec C1000A, C1900A, C2000A, C2300A, C3000A; Adtran C424G; Technicolor C2000T, C2100T; Zyxel C1100Z, C2100Z, C3000Z | Code matching the vulnerable pattern |
| CenturyLink | Actiontec Q1000, Zyxel Q1000Z | Component only, no match for the flaw |
| Frontier | Actiontec F2250 | Code matching the vulnerable pattern |
| Comcast (Xfinity) | ARRIS/CommScope X5001, listed as XF3 | Code matching the vulnerable pattern, in firmware from a 2022 archive |
The list also includes gear sold in the US without a provider attached. It names North American versions of two older Netgear modem-routers, the DGND3700v2 and DGND4000. TP-Link’s Archer C3150 V2 with US firmware is there too, along with several Cisco small-business routers.
This is the US answer that early coverage missed, and it needs a careful reading. A firmware scan is a strong signal, not a demonstration. Kaiser calls his scanning rules “triage aids” and warns that a patched file can still trip them. The list also can’t tell you which firmware your own gateway runs today.
So here’s the fair reading. These models shipped Broadcom’s vulnerable code at some point, and their providers now owe customers a clear answer.
Broadcom says a fix exists, but it hasn’t reached homes
Kaiser reported the bug to Broadcom on July 18 and July 27, his disclosure timeline shows. On July 28 Broadcom told him a patch was available and that device makers should contact the company. It then refused to register a CVE, the standard ID that security teams use to track fixes.
That refusal had a knock-on effect. Kaiser opened a case with the CERT Coordination Center on August 4, and it closed the same day. Broadcom is itself a CVE numbering authority, and it hadn’t assigned one.
Broadcom moved away from the old WPS code in 2018, according to Kaiser’s public FAQ page. It reportedly declined a CVE because the software is outside its support window. We found no public Broadcom statement or advisory. TechSpot and The Hacker News also paraphrased its position rather than quoting it.
Kaiser calls the oldest affected chips a “definitive forever day,” meaning he expects no fix for them.
The pattern looks a lot like the PHP2Shell flaw we explained this week. The company that wrote the code says a fix exists, and someone else has to ship it. For routers, that’s your provider or the brand on the box, and many of the listed models are years old.
Kaiser says he knows of no real-world attacks using the flaw, The Hacker News reported. A translated PCWorld article said it was being exploited, but we found no evidence of that anywhere else.
What to do with your router tonight
Your router guards every device behind it, including smart TVs like the LG sets caught scanning home networks. These steps apply whether or not your model is on the list:
- Find your model name on the label, usually on the back or bottom. AT&T’s BGW210 also has it printed on the front. Compare it with Kaiser’s list, but a missing model isn’t proof of safety.
- Turn off WPS in the router’s admin settings. CISA’s home network security guide already says to “Disable Wi-Fi Protected Setup (WPS).” Treat it as a stopgap. Kaiser warns that a settings toggle “may not remove or fully disable the vulnerable parser.”
- Update the firmware. CISA says to check the maker’s website for the latest version, and some routers update themselves. Kaiser’s FAQ suggests asking your provider whether an update fixes this specific issue.
- If no fix comes, TechSpot suggests turning off the gateway’s Wi-Fi and switching it to bridge mode. You’d then run your own up-to-date router behind it.
Changing your Wi-Fi password won’t help here, TechSpot notes, because the flaw is reachable before a device logs in. Older home gear matters beyond your own house, too, as our explainer on the FBI’s botnet cleanup showed.
Belgium moved within days, but US providers haven’t spoken
Switching WPS off seems to blunt the risk. Kaiser’s toolkit reports that a router not advertising WPS isn’t affected, and that’s the fix Belgium’s biggest provider chose first. Proximus turned off WPS across its whole fleet within about 24 hours, Kaiser wrote on October 20. It plans full patching in the coming weeks.
Orange Belgium is looking at doing the same, he wrote, while Telenet checked its fleet and isn’t affected. We found no public statement on the flaw from AT&T, CenturyLink, Frontier or Comcast as of October 24. AT&T’s BGW210 support page still explains the gateway’s WPS light, with no mention of the issue.
Kaiser is still adding devices through GitHub, and anyone can submit a model with firmware evidence. The next test is whether the four US providers publish firmware notes for the listed models. They could also follow Proximus and switch WPS off remotely.