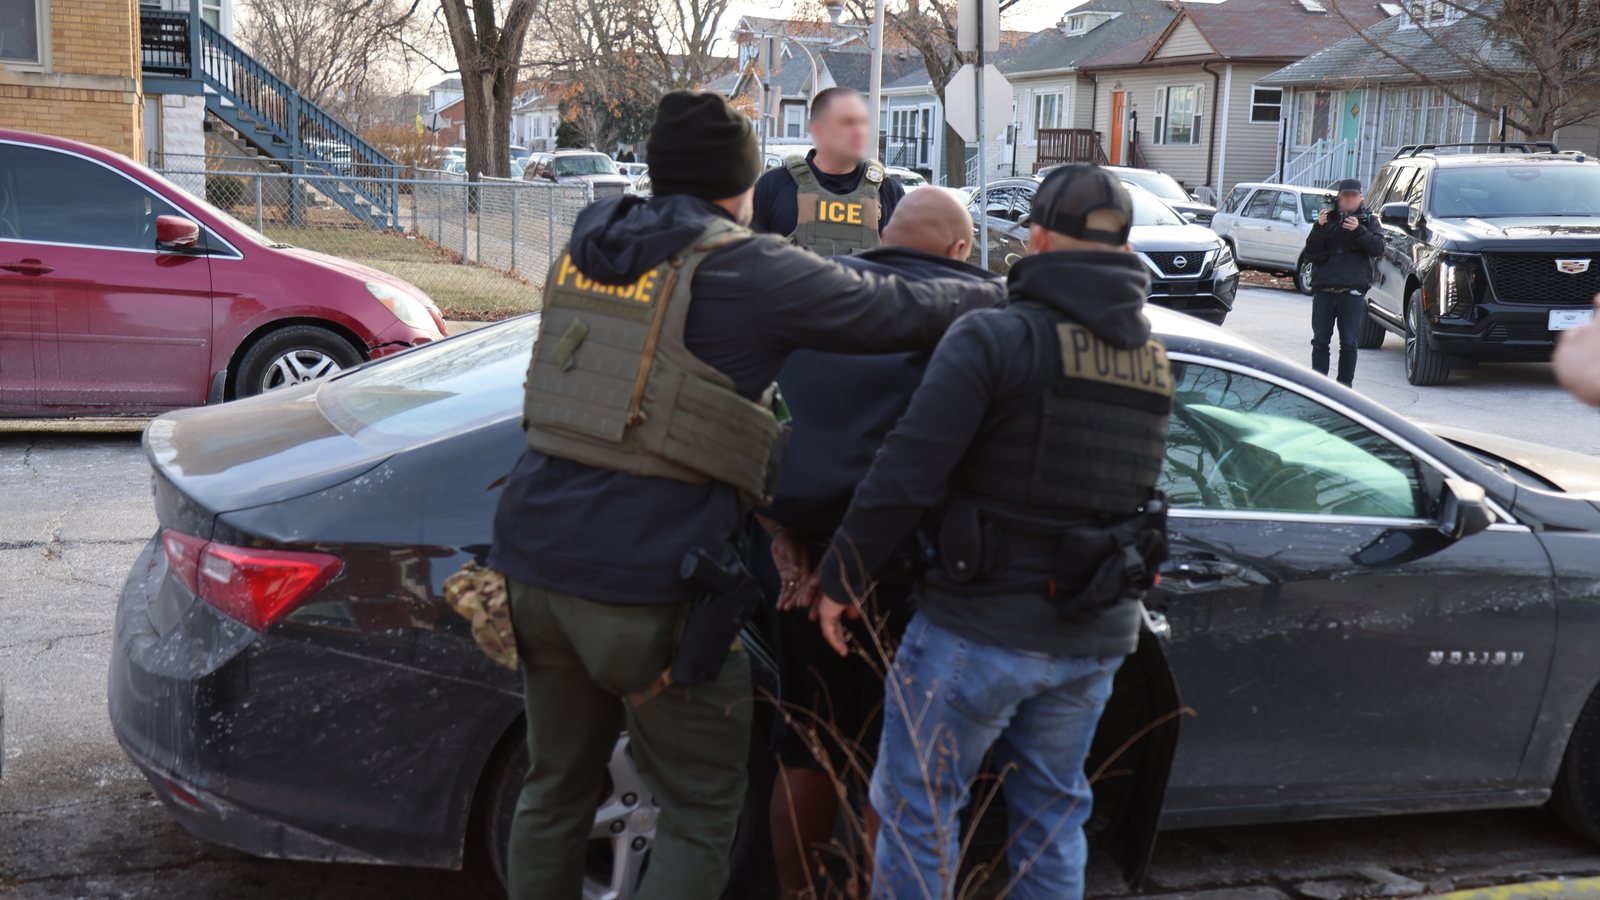
A DHS data leak published on Wednesday, October 28, lists more than 41,000 Department of Homeland Security employees and contractors. About 10,000 of them are tied to Immigration and Customs Enforcement, WIRED reported, and more than 21,000 work for Customs and Border Protection.
The transparency nonprofit Distributed Denial of Secrets released the archive, which it calls Icepick. It credits a hacktivist group calling itself the Department of Peace.
DHS has not confirmed the files are authentic. A spokesperson said the department is “aware of a potential breach and is actively working to address the situation swiftly and effectively.” Reuters and TechCrunch matched entries to known DHS employees and third-party records, Politico reported.
The leak goes beyond a staff list. It sketches how the agency behind Trump’s deportation drive is organized, from headquarters down to field agents. DHS carried out 980,000 deportations in the first 18 months of Trump’s second term, according to the Migration Policy Institute, as CNBC noted. It also reopens a legal fight over whether naming federal officers is accountability or doxing.
CBP and ICE make up most of the 41,000 records
The records include names, offices, contact details and job assignments, CNBC reported. The BBC described work addresses, phone numbers and descriptions of each person’s work. WIRED said the files list workers’ cell phone numbers and the locations of ICE and CBP facilities. They were last updated on August 19, 2026.
By WIRED’s count, CBP accounts for more than half of the records. ICE has about 10,000, roughly a third of them in Homeland Security Investigations, its investigative arm.
Another 6,200 belong to U.S. Citizenship and Immigration Services, and nearly 1,000 to the Cybersecurity and Infrastructure Security Agency.
The archive is not complete. NPR put it at about a fifth of a DHS workforce of a little more than 220,000, while WIRED’s estimate was closer to a seventh. DDoSecrets co-founder Emma Best said “Icepick identifies many of the architects and drivers of DHS policy and operations” rather than every employee.
Undercover units, wiretap programs and face-recognition users
The more revealing part is the permission groups, which control who can reach which internal systems. WIRED counted more than 55,000 group names. At HSI, 39 employees across more than a dozen field offices sit in groups marked “CUC,” which court filings say stands for “certified undercover operation.” Other groups reference a wiretap program and tools for pulling data from seized phones.
More than 200 CBP accounts belong to a group for Mobile Fortify, the face-recognition app immigration agents use to identify people. Politico put that figure at no fewer than 217. Roughly 1,300 ICE enforcement accounts were created after July 4, 2025, when Trump signed the One Big Beautiful Bill Act, which funded 10,000 new ICE enforcement and removal officers.
Most records also name a supervisor. That lets anyone reconstruct reporting lines across the department. BreezyScroll has not reviewed the files and is not naming anyone in them.
How a sign-on system could hand over an org chart
DDoSecrets says the data came from DHS’s Okta login system. Okta runs single sign-on, the service that lets one employee login open many work apps. To do that, it keeps a directory of users and the groups that decide what each person can reach.
That matches what WIRED and the BBC describe in Icepick: names, titles, supervisors, contact details and access groups.
Okta denies a breach on its side. “We are aware of this report. Okta is secure, and we have no evidence our data or systems were compromised,” a spokesperson told WIRED.
The two claims are not necessarily in conflict. A stolen DHS login or a misused account inside DHS’s own setup could expose the department’s directory without any break-in at Okta. Neither DHS nor the hackers have said how the data left, and the Okta route remains a claim.
Security researchers see the risk in the structure itself. “If authentic and current, this is an extraordinarily valuable intelligence resource for those seeking to penetrate DHS,” Alexander Leslie of the threat intelligence firm Recorded Future told WIRED. He warned that an adversary could use it to “develop convincing impersonation attempts.”
Names and reporting lines are what make phishing believable, the same social-engineering logic behind the fake CAPTCHA “Windows+R” scam we explained this month.
The group behind Icepick has hit DHS before
The Department of Peace is not new to DHS. In March, a group using the same name claimed a hack of DHS’s Office of Industry Partnership and released contract data on more than 6,000 companies through DDoSecrets, TechCrunch reported.
This time the group tied the leak to DHS Secretary Markwayne Mullin. “On July 17th, Markwayne Mullin said he was ‘turning up the heat.’ This is what happens to ICE when you do that,” a spokesperson said, according to NPR. A note included with the files reads: “They have our information, so it’s only fair that we have theirs.”
The people who published it frame the leak as oversight. “We need oversight for useful government, if it exists at all,” Ryan Ottignon, a journalist who helped build a searchable version, told NPR.
The leak caps a bad autumn for federal systems. Politico reported breaches of Pentagon and FBI personnel systems in September, and the Federal Election Commission’s electronic filing system went offline after an attempted hack in October.
WIRED noted that ShinyHunters claimed data on nearly every FBI employee, and law enforcement has since arrested several suspects. Those incidents came alongside the wave of flaws we sorted through in our Black October hacks explainer.
When publishing officers’ details becomes a federal crime
The main federal law here is 18 U.S.C. 119. It bars knowingly publishing “restricted personal information” about a covered person to threaten, intimidate or incite violence against them, or knowing it will be used that way. The penalty is up to five years in prison.
The definitions narrow it. “Restricted personal information” means a Social Security number, home address, home phone, mobile phone number, personal email or home fax. “Covered person” includes any federal officer or employee, through 18 U.S.C. 1114.
So the law turns on the kind of data and the intent. Names, titles and office locations are not on the list. Mobile numbers are, and WIRED said the files include cell numbers, without saying whether they are personal or work phones.
Adam Steinbaugh, a senior attorney at the civil liberties group FIRE, told WIRED the administration takes an expansive view of the law. “This is information that would be on a business card,” he said. “That’s not something the government can criminalize.”
DHS reads the issue differently. In a January press release, it warned: “if you lay a hand on a law enforcement officer or dox our officers, you will be prosecuted to the fullest extent of the law.” WIRED reported that DHS has widened its own definition of doxing to cover names and titles. In June, prosecutors charged 15 Minnesota residents under stalking and threat laws tied to anti-ICE activity.
The hackers and the outlets reporting on them also stand on different ground. In Bartnicki v. Vopper (2001), the Supreme Court protected publishers who played no part in an illegal interception, obtained the material lawfully and reported on a matter of public concern. The Court expressly left open the case of people who obtained the material unlawfully themselves.
The questions DHS has yet to answer
The FBI referred WIRED’s questions to DHS. DHS has not said how the files left its systems, whether the Okta claim holds, or whether anyone in the dataset faces new security measures.
The August 19 cutoff also matters. The files would miss anyone hired since then and could still list people who have left. DHS said it will “update the public when more information is available.” It has not said when that will be.